How to identify and prioritize critical software updates on Windows and Linux
A practical, risk-based process for prioritizing Windows and Linux updates, with version-aware guidance and clear limits where Linux details are unavailable.
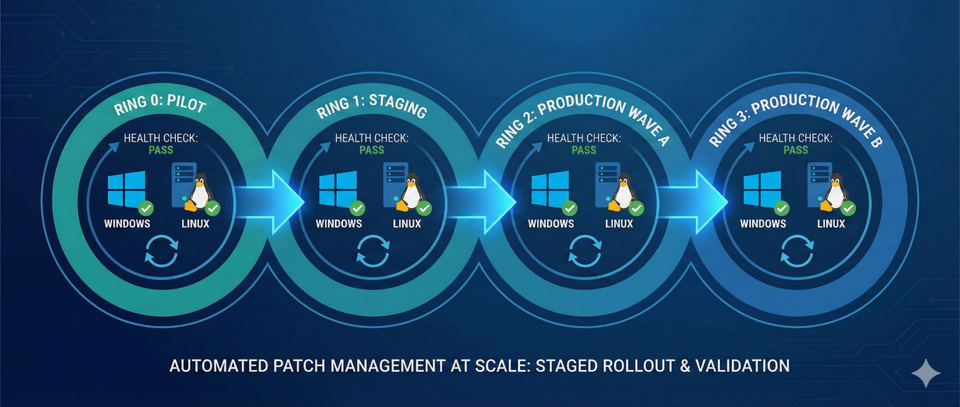
Start by listing the operating systems, versions, installed software, and the devices or services each one exposes. Then check trusted vendor update guidance and prioritize updates that address actively exploited vulnerabilities or affect systems exposed to untrusted content or network traffic.
Prerequisites
Know which Windows version or Linux distribution and release each device runs. Update instructions and available fixes can differ by version.
Verify a current backup before starting updates. Confirm that important files are included and that you can access the backup. This guide does not assume a particular backup or recovery method.
For managed devices, coordinate timing with the person responsible for deployment.
Prioritize updates by risk
Check for active exploitation and vendor urgency. Put updates addressing vulnerabilities known to be exploited, or identified by the vendor as urgent, near the top of the queue.
Confirm exposure and use. Give more attention to affected software that is reachable from the internet or other untrusted networks, handles untrusted files or messages, or runs with elevated privileges. A system's role and how people use it matter; a severity label alone does not capture your environment's risk.
Review each vulnerability individually. Compare severity with exploitability, attack path, required privileges, user interaction, affected version, and your device's exposure. Vulnerabilities grouped together for analysis can still have different risk levels.
Schedule and verify deployment. Apply the relevant vendor-supported update to affected devices, then check that installation completed and review any vendor follow-up guidance. Don't assume an update applies to every version or product in your inventory.
Microsoft describes “risk cohorts” as an exploratory way to group vulnerabilities around shared environment questions. They are not official vulnerability categories and do not replace reviewing individual vulnerabilities or Microsoft guidance. Read Microsoft's explanation of risk-based prioritization.
Windows
Use Microsoft's Windows update guidance for your installed Windows version. The supplied Microsoft support page is a general Windows help and learning entry point, not a version-specific set of installation steps. Its separate technical article includes legacy Windows XP instructions, so do not treat those old menu paths or Internet Explorer steps as current guidance for supported Windows versions. For help with Windows updates, start at Microsoft Windows help and learning.
Linux
The supplied sources do not include Linux distribution-specific update instructions. Identify the exact distribution and release, then consult that distribution's official security advisories and update documentation. Follow its supported package-management process; exact commands and interface labels vary, so this guide does not provide commands that cannot be verified from the supplied material.
Troubleshooting
The update doesn't appear: Check the vendor's guidance for the exact product and version. Don't install a package intended for another release.
The device is managed: Ask the administrator about deployment timing and applicable policies before making changes.
Installation fails or the device behaves unexpectedly: Stop repeated attempts, record the version and error message, and use the vendor's official support guidance. For Windows, use Microsoft Windows help and learning.
You are unsure which issue to fix first: Recheck active-exploitation notices, affected versions, exposure, and privileges. Avoid relying on a broad grouping or severity score as the only decision factor.
For broader preparation, see how to protect your computer and data from cyber attacks.